Hackers, from technological evolution to government weapons
According to Wikipedia, when we talk about a hacker we are referring to the person with “advanced skills in computing, an expert capable of entering a computer and its networks through system vulnerabilities”...
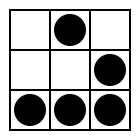
What are hackers?
According to Wikipedia, when we talk about a hacker we are referring to the person with "advanced skills in computing, an expert capable of entering a computer and their networks through system vulnerabilities"However, far from this obscure definition, hacker culture was born thanks to the enthusiasm of those who constantly look for ways to improve technology by finding weak points in software, hardware or procedures. The hacker is not only an expert in finding the most insecure parts of the system, but also offers improvements and solutions to the defects he has found.
In addition to this, hacker culture encompasses the creation of communities and subcultures using different communication channels such as forums and chats where ideas are exchanged and technical topics are discussed. But not all hackers work in the same way, which is why it is common to classify them into three groups. We will also talk about those who do not fall into any of the following groups.
White hat hackers are, above all, ethical people who use their skills to improve systems, computer programs and methods to create a secure environment for data and the internet in general. These hackers are constantly clashing with their rivals, the black hats. Bad guys who use their skills to carry out criminal acts.
Normally, white hat hackers are highly rewarded for their work and there are rarely cases in which they put their jobs at risk since, once they find a vulnerability, they reach agreements with the clients and employees they work with. Likewise, it is also widely accepted that its purpose is to make the Internet and technology in general safer places.
However, the nature of black hat hackers It's dangerous. They are governed by dishonest actions such as making money illegally or present themselves as technological assassins for hire. Their motivations are harmful to the field of computing not only because they lack principles, but also because they do not reveal their discoveries to those affected, but to the community to which they belong. In short, the attacks they carry out do not improve the environment at all and, on the contrary, maintain vulnerabilities for future attacks.
Because black hat hackers share the same name (hacker) with the group that is motivated by ethical motivations, the latter refer to the others as "crackers" with the intention of not identifying them with those who commit criminal acts. Therefore, if you talk about a "hacker" simply referring to a "black hat hacker" you may see the anger reflected on the face of an ethical or white hat hacker.
As if that were not enough, there is a third classification of hackers, those with hats grey, which basically refer to individuals whose work could not be classified as bad, but they are not saints either. Their hacking exploits are motivated by pure fun and desire to "troll", however, in some cases their actions border the limits of legality.
And hackers have been found who act as double agents when choosing between improving or destroying systems, software or methodologies based on political factors, social principles or economic interests. An example of this is found in white hat hackers who are not well paid and easily forget their ethical nature depending on the circumstances.
But there is a classification of hackers that most websites ignore because it is a relatively new concept and one that began to be talked about a few years ago.
behind the scenes, For governments and states around the world, hackers are hired to defend the interests of the "client", which in other words is about carrying out dirty tasks. Within the field of technology, such tasks are often considered an offensive to security. To understand this and based on recent events, hackers hired by governments can be from any of the groups we have mentioned, since the concept of national security is (erroneous in my opinion) placed above any regulation or law.
USA
In 2009 the United States government undertook a cyber defense project called USCYBERCOM. The infrastructure of the National Security Agency (NSA) was integrated into it. Additionally, the project was physically housed in the same facility as the NSA in Fort Meade, Maryland, and thanks to declassified public documents, we know that it also shares the same computers and networks as the NSA.
Among the technology community and in the eyes of the world's media, this project was perceived as an offensive force and for years the State has not had sufficient arguments to prove the opposite while it has been operating.
According to the United States Department of Defense, USCYBERCOM "plans, coordinates, integrates, synchronizes and conducts activities that: direct operations and protect specific information of the Department of Defense and are also prepared to, when indicated, conduct military operations in cyberspace in order to enable actions in all domains and ensure the freedom of the United States and Allies in cyberspace, while repelling the actions of its adversaries." USCYBERCOM is sub-unified with the United States Strategic Command unit, the same institution responsible for the country's nuclear weapons strategy.
In 2008, a classified NSA document called the "NSA ANT Summary" was leaked by an anonymous source. This event revealed to the international community the offensive cyber technology that the NSA used to spy on its adversaries. My intention is not to go into many details, but to demonstrate their importance through 2 short examples of events that are related to each other and were a consequence of the leak of this summary.
One of them is the concept of BadUSB. The first time its existence was made known was through the BadUSB concept, a vulnerable USB protocol that still upsets the cybersecurity community.
The code name COTTONMOUTH describes a family of USB Hardware Host Tap electronic devices hidden in a USB Type A connector, USB hub, or USB connector depending on the versions of COTTONMOUTH [1-2-3] described in the NSA "toy" summary. The device's capabilities are defined as "a USB (Universal Serial Bus) hardware implant that provides a wireless bridge into a target network as well as the ability to load rogue software." on the destination PCs." After the leak of the documents in 2008 and inspired by COTTONMOUTH, security experts were able to replicate the vulnerability and some companies like Hak5 began to market their own versions of the NSA COTTONMOUTH. Among the best-known products was the Rubber Ducky, which was launched as a proof of concept in 2010.
It is important to note that the NSA was already using this device in 2007 (as the ANT summary suggests) but a commercial version was only available to the public three years later, a fairly long delay between military access and civilian access to new technologies.
HEADWATER was another controversial product that was in the ANT summary. It was presented as an advanced persistent threat (APT) exploit for Huawei routers. As a matter of fact, Huawei is a Chinese multinational founded by a former officer of the People's Liberation Army and established itself in the market as a world leader in industrial networks.
This attracted the attention of the NSA due to the great reach (and threat) that Huawei products were achieving around the world, but also due to the use of this brand's products in China's data infrastructure. Let us remember that in political matters, China has been considered a rival to the United States throughout history. Furthermore, the NSA's interest in Huawei is also justified by the possibility that the Chinese intentionally implemented potential backdoors in the products that Huawei marketed, which would leave the Internet vulnerable to Chinese cyberespionage.
The HEADWATER dates back to 2008 and arrived suspiciously after a alleged NSA hack of Huawei infrastructure. This fact, dated 2007 was documented in the leaked papers through an operation confirmed by Edward Snowden, the famous NSA whistleblower who defected in 2013 and has since obtained political asylum in Russia.
The fact that HEADWATER occurred a year after the NSA's covert operations against Huawei's infrastructure could mean that the HEADWATER backdoor is a white-box analysis product made by the NSA on top of source code stolen in the alleged attack on Huawei. Although the temporal correlation of the events does not prove anything, it cannot be denied that it is curious and, at the very least, suspicious.
CHINA
However, the United States is not the only country that has taken computer attack operations to a military level. In February 2013, a cybersecurity company called Mandiant, which was acquired by FireEye (a leading global cybersecurity company that advises on national security to the United States) for more than $1 billion, published a report on APT1, a cyberespionage unit of the Chinese People's Liberation Army whose 5 members were convicted in "absence" by a Grand Jury of the Western District of Pennsylvania, USA. The news had global reach since it was the first trial of its kind in the United States. The APT1 report It is an important piece in the security industry, a good example to follow for cybersecurity professionals around the world..
The Mandiant report is a compilation of evidence on the existence of the Chinese People's Liberation Army group, PLA Military unit 61398 (official name of the Chinese militarized unit). The title of the report, "APT1, Describing a Chinese Cyberespionage Unit," raised international fears that APT1 was not the only Chinese unit operating for these purposes.
Additionally, the Mandiant report, whose findings spanned three years, has given the international community a detailed look at China's cyber operations, the involvement of the Chinese People's Liberation Army, as well as the facilities, technologies, skills and tools used by the APT1 group, among other things.
The use of RATs, social engineering and an extremely organized attack infrastructure with resources that the Mandiant report includes as "state project resources", which APT1 infiltrated to steal confidential data.
It was also learned that during these attacks the APT1 group obtained information that gave the Chinese government an advantage in producing cheaper technology that could compete against the hacked entities in the United States.
A leading global steel manufacturing company, US Steel, was allegedly penetrated by this same group. In 2011, APT1 was continuously spying on the multinational steel producer's infrastructure for approximately 3 years until the Mandiant report was published.
Another aspect mentioned in the report is the impressive level of organization of the Chinese group's operating units around the world, which was reflected in the purchase of high-speed fiber optic broadband as well as IPv4 ranges from China Telecom by the Chinese Army to provide technical assistance to the group. Everything is demonstrated in the Mandiant report through evidence such as commercial invoices, images of facilities and structures, as well as attack logs, among others.
RUSSIA
It wasn't long ago that a sysadmin complained on a forum that some of the servers he was managing were hacked and the file structure was a mess. He suspected it was the work of Russian hackers. Then a member of the forum responded that "it could be anyone, except the Russians." It was when the person affected by the alleged hacking asked how he knew that, to which he replied that "if it had been the Russians, this conversation would not have happened because you would not have known that you had been hacked."
Although the presence of hackers backed by the Russian State is well known throughout the world since much has been written about it in the international media, few facts have been established about Russian cyberwar units due to the high level of secrecy and the lack of public statements on the subject.
Obviously secrecy represents a great advantage in this line of work. In 2014, Sergey Shoigu, Russian Defense Minister announced a hacker recruitment program, backed by $500 million in public funds. And although the structure of Russian cyberwarfare units has never been revealed by Moscow, it is known that these entities are sub-unified under the structure of Russian Military Intelligence (GRU).
Recent statements by United States officials suggest that senior leaders around the president participated in the DNC hack.. Russian APT groups used names such as Fancy Bear and Cozy Bear and their existence was always denied by Russian leaders. In fact, the unethical actions attributed to them were condemned by the security community, however no expert dares to discuss the professional skills of these cyber thugs.
The truth is that they are seen as the best hackers in the world. Their stealthy actions could go unnoticed as long as the impact of the attack was not so noticeable. A recent attack on the US National Democratic Council is believed to have directly influenced the American elections. Something enormous taking into account not only the power that a country like the United States has in the world, but also because it is unknown that anyone has ever had such a level of influence in the internal affairs of the United States.
"An act of war" was how the leaders of the Republican party presented the alleged hack of the National Democracy Committee that was apparently made possible using one of the oldest tricks in the hacking manuals: phishing. But what matters is not what the hack meant, but the purpose and if confirmed (as far as I know, not much has been proven yet) the Russian hackers accomplished their mission at unprecedented levels in the world of cybersecurity.
ISRAEL
Another notable example of countries that use cyber units within their military organization is Israel, whose presence in the cyberwar theater became known for the first time in the "Stuxnet" case. In the documentary "0 days," members of the United States administration admitted the Israel-US union in a cyber mission in which centrifuges used in the Iranian nuclear program to enrich uranium were infected and destroyed. Some evidence suggests that Israel has a representative in the theater of global cyberwar, known as Special Unit 8200, a military unit directed by the army and whose members are considered a state secret. Its base is located on Avital Mountain.
HOW DO THEY DO IT?
Although technological advances produce new tools and methodologies every day, the largest computer attacks occur in a simple way, with techniques that are already known. However, there is a big difference between hacking your neighbor's blog and breaching the security of an American political leader, or even hacking the NSA itself. So what makes covert hackers such efficient weapons? There are several factors to take into account to know.
A company that needs hackers will have a very limited search range of influence such as the geographical factor, its financial capacity or the platforms on which it offers its jobs. On the other hand, a government has a global reach, its financial capacity is enormous compared to most corporate entities and, furthermore, its ability to organize national contracting programs and activities that support it is an advantage that is not within the reach of a company. (security conferences, hacking competitions, education events in schools and universities). It is worth talking about patriotism, another of the important factors when forming armies around the world.
Although it has been continually denied by governments, another channel for recruiting hackers is the conversion of black hat hackers convicted through pardon. Imagine a hacker who has been caught carrying out a criminal act and before he completes his sentence he receives an offer that the army that has arrested him cannot refuse. "Work for us and we will forget everything you have done." If you think this only happens in movies, we can take a look at the next article where a clear parallel is seen between the pardon of a hacker and the expansion of USCYBERCOM.
When a hacker is hired, the government agency's mission is to help him be as efficient as possible to accomplish the task he must perform. From my point of view, there is a determining factor that is mixing operational intelligence with computer security experts. An attack is much more efficient when it is carried out from various angles, that is, from the real and virtual world.
A hacker who attacks an entity remotely is limited by the level of defense that said entity has and there are organizations that are impossible to hack from the outside, simply because their most critical parts are not connected to the Internet. And when a hacker fails to break in remotely, his job ends there. For this reason, the intelligence service supports it with resources and physical capabilities, infiltrating the core of the organization.
These intelligence operatives adhere to a position that allows them to physically access the central infrastructure of the computers and help with the resources provided by the intelligence services that have hired them. This is when a remote control device is implanted within the network that opens communication with the computer expert operating from afar and that's it! We only have to go back for a moment to the NSA spy devices catalog to understand that this tactic exists.
For example, a Maryland NSA instance is never hacked in the classic way or at least there is no evidence that such a breach of its security has taken place. However, You just have to take a look at the impact Snowden had on his agency. Obviously, it is easier to hack an entity from the inside than from the outside.
ARE WE REALLY HELPLESS?
So what can companies, organizations and governments do to protect yourself from undercover hackers? Are we really helpless against the destructive power of these virtual bullies? Well, there is something we must remember: the eminence with magical powers in hacking is nothing more than a legend, just like in real life. A company that respects safety principles , who reviews the past of his new employees, who train and educate your employees with practical examples of attacks, which maintains its tightly closed servers and? audit your security frequently simulating attacks and new threats is less likely to be seen in a serious security problem. However, a hacker will always keep looking for new ways to break in and attack his competitors' protection and will see it as a game of chess at the highest level. So in the future, keep your firewalls up to date, lower your confidence level and prepare for the future of cyber wars. Never doubt that we are already living one, we have been doing it since the first day we connected to the network.
Need Help Applying This?
If this topic relates to your environment, we can scope the right engagement model and provide a clear plan with evidence-focused outcomes.