Shieldbox
Formerly documented as ODS Sandbox, Shieldbox is a secure intermediary device for handling untrusted USB media without exposing endpoint computers directly.
What It Is
Shieldbox is designed as a hardware-in-the-middle control layer between untrusted external USB devices and trusted user workstations. Instead of plugging unknown storage directly into a laptop or desktop, files are first processed through a dedicated, isolated unit.
The objective is straightforward: reduce infection risk from malicious USB-borne payloads while keeping file transfer workflows operational for public administration, enterprise, and high-volume file handling environments.
How Shieldbox Works
- Connect Shieldbox to the workstation (USB, Wi-Fi, or Ethernet-supported modes in product docs).
- Open the local interface from browser or desktop pathway.
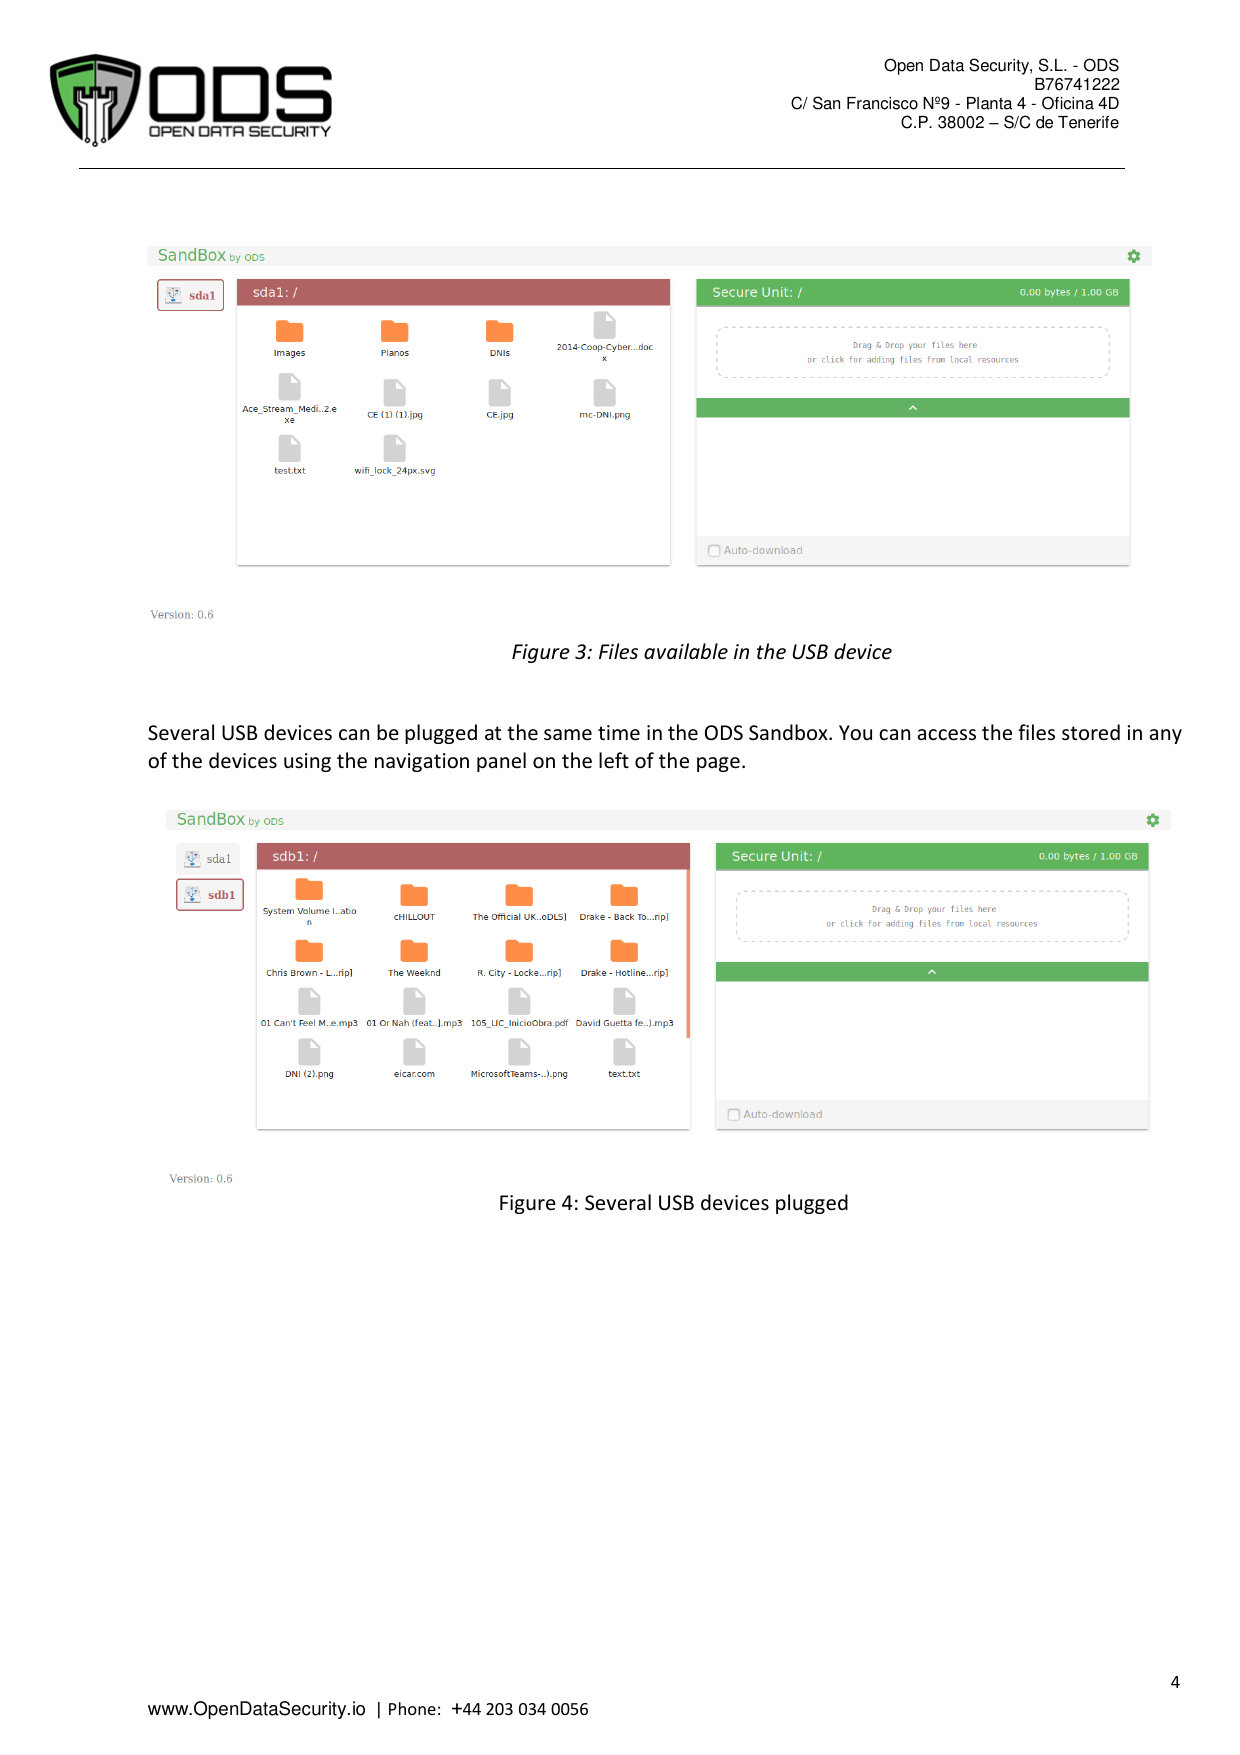
- Plug one or more untrusted USB devices into Shieldbox.
- Select files to analyse and transfer into the secure unit.
- Integrated malware scanning validates selected files before release.
- Safe files are downloaded or copied onward; infected files are blocked.
- Infection events produce report output for user review and handling.
Capabilities Documented in the Product Material
- Plug-and-play usage with no complex endpoint setup.
- Support for multiple concurrent USB devices in one workflow.
- Local file scanning via drag-and-drop before sharing.
- Secure transfer channel with encrypted communications.
- Online and offline update pathways for software and signatures.
- Cross-platform compatibility for Windows, macOS, and Linux estates.

See More ODS Labs Projects
Explore the broader R&D catalogue and current public concepts from the labs programme.